VerSprite Blog
Literary Antidotes for Today's Security Snake Oil
Explore the latest insights and stay informed on evolving digital threats
Category
- All Resources
- Advanced Threat Modeling
- AI
- Application Security
- Automated Threat Modeling
- Cloud Security
- Compliance Automation
- DevSecOps
- Digital Forensics & Incident Response
- eBook
- In The News
- Information Security Management System (ISMS)
- Integrated Risk Management (IRM)
- Managed Detection and Response (MDR)
- Mobile Security Testing
- News
- OffSec
- Penetration Testing
- Red Teaming and Social Engineering
- Reports
- Security Governance
- Security Operations
- Security Research
- Security Testing
- Security Training
- Supply Chains
- Threat & Vulnerability Management
- Threat Intelligence
- Threat Modeling
- Threat Report
Follow Us


Threat Modeling
How Advanced Threat Modeling Helps CISOs Prioritize AI, Cloud & Third-Party Risk in 2026
Compliance Automation
Continuous Audit Evidence Automation for SOC 2, PCI DSS, and FedRAMP
Application Security
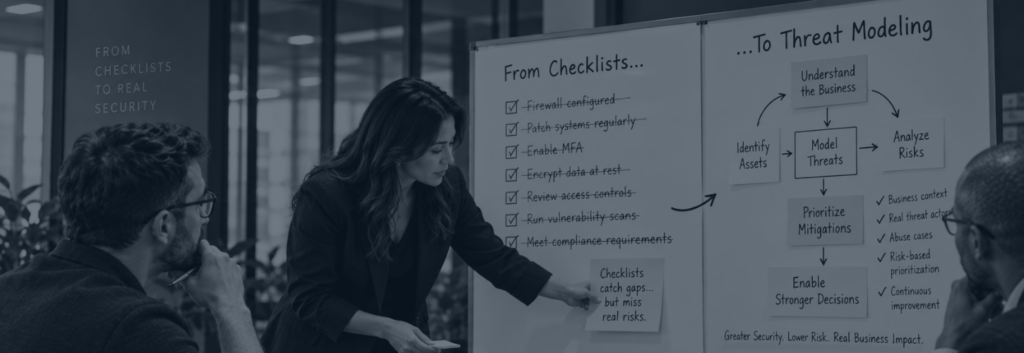
From Control Validation to Risk Understanding: The Case for Threat Modeling
Threat Modeling
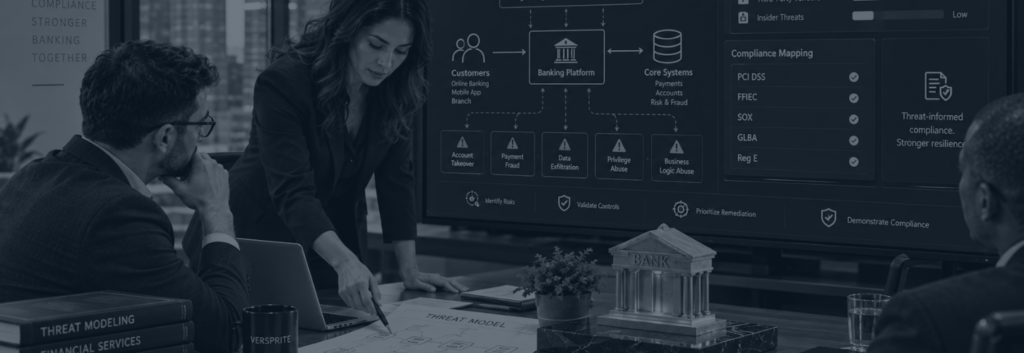
Banking Threat Modeling Services for Compliance
AI, In The News
VerSprite Becomes a CREST AI Charter Signatory
Application Security, Threat Modeling
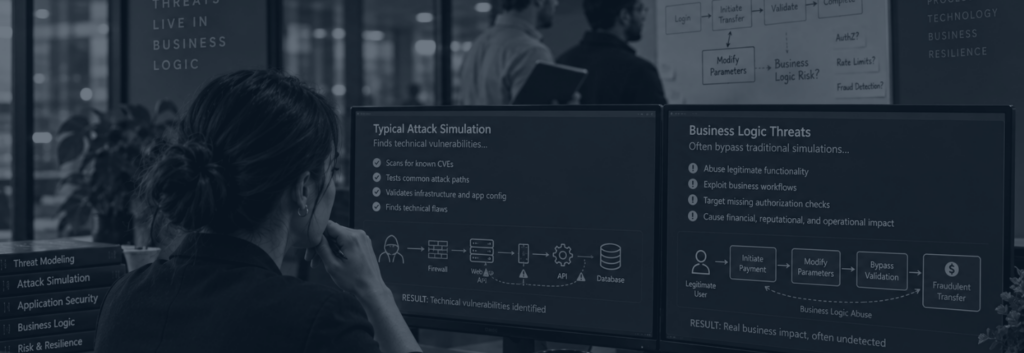
Why Attack Simulations Miss Business Logic Threats
Threat Modeling
7 Threat Modeling Services for Risk-Based Remediation
Mobile Security Testing, Security Governance, Threat Modeling
Scaling Threat Modeling for Banking Apps
Threat Modeling
9 Threat Modeling Deliverables CISOs Should Demand
AI, Regulatory Compliance, Security Governance
Compliance Automation for AI Security: Why Manual Evidence Collection Weakens Cloud Security
Penetration Testing
What Is Penetration Testing as a Service?
AI
How AI Tools Are Compounding Third-Party Risk (And How To Manage It)
Security Operations
AI-Driven SecOps with Gemini: What Changes in SOC Operations
Penetration Testing, Security Testing
ZANCUDO: Open-Source MQTT Interception Proxy for IoT Pentesting
Integrated Risk Management (IRM), Security Operations
