Healthcare Cybersecurity Solutions
Protecting What Matters Most:
Patient Safety, Clinical Operations & Sensitive Health Data
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
What Is Healthcare Cybersecurity?
Healthcare cybersecurity is the practice of protecting patient data, clinical systems, and connected medical devices from cyber threats — with the defining requirement that security must preserve patient safety and clinical continuity, not just data confidentiality. Unlike general cybersecurity, a healthcare program has to account for environments where a control that blocks an attacker could also block a clinician from reaching patient records in an emergency. Effective healthcare cybersecurity therefore combines threat modeling, penetration testing, medical-device security, and regulatory compliance (HIPAA, HITRUST, FDA) around a single priority: keeping patients safe.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
The Stakes in Healthcare Are Higher Than Any Other Industry
In healthcare, a cybersecurity failure isn’t just a data breach — it can be a threat to human life. Ransomware attacks have diverted ambulances, delayed surgeries, and disrupted life-sustaining medical devices. At VerSprite, we recognize that while data privacy is essential, patient safety must always come first.
For over 20 years, VerSprite has partnered with healthcare organizations across the care continuum — from the world’s largest medical device manufacturers to regional health systems, healthtech innovators, and healthcare payers. We understand that healthcare cybersecurity requires more than checkbox compliance; it demands a risk-centric approach that prioritizes clinical continuity and patient outcomes
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
The Healthcare Threat Landscape
Healthcare remains the most targeted critical-infrastructure sector in the United States:
- $7.42 million is the average cost of a healthcare data breach in 2025, the highest of any industry for the 15th consecutive year (IBM Cost of a Data Breach Report 2025).
- 279 days is the average time for healthcare organizations to identify and contain a breach, nearly six weeks longer than the global average (IBM Cost of a Data Breach Report 2025). (New, current, highly citable stat.)
- 259 million Americans had protected health information (PHI) exposed in 2024.
- 72% of healthcare organizations reported patient-care disruptions from cyberattacks in the past year.
- Ransomware against healthcare continues to rise year over year.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Who We Serve
Healthcare Insurance & Payers
Health insurers, pharmacy benefit managers, and claims processors handling vast volumes of PHI and financial transactions under complex regulatory requirements.
Healthcare Organizations (HCOs)
Hospitals, health systems, clinics, dental practices, ambulatory surgery centers, and other providers delivering direct patient care across physical and virtual settings.
HealthTech & Digital Health
Software companies building patient portals, analytics platforms, telehealth solutions, wearables, implantables, and AI-powered clinical decision support tools.
Healthcare Manufacturers
Medical device manufacturers, pharmaceutical companies, and healthcare equipment producers subject to FDA cybersecurity requirements.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Why Healthcare Organizations Choose VerSprite
Patient Safety as the North Star
Every security recommendation considers clinical impact. We don’t propose controls that would impede care delivery or create patient-safety risks. Our threat models account for clinical workflows, not just technical vulnerabilities.
20+ Years of Healthcare Expertise
We’ve been securing healthcare organizations since before HITECH existed. Our team includes professionals with deep experience in healthcare operations, clinical environments, and the regulatory landscape.
Regulatory Mastery: HIPAA, FDA & Beyond
We help you build security programs that actually protect patients and data, aligned to the HIPAA Security & Privacy Rules, the HITECH Act, HITRUST CSF, FDA Cybersecurity Guidance (Section 524B, premarket submissions, SBOM requirements), NIST 800-66, and international frameworks (PIPEDA, GDPR).
Regulatory Compliance →
Risk-Centric Threat Modeling with PASTA
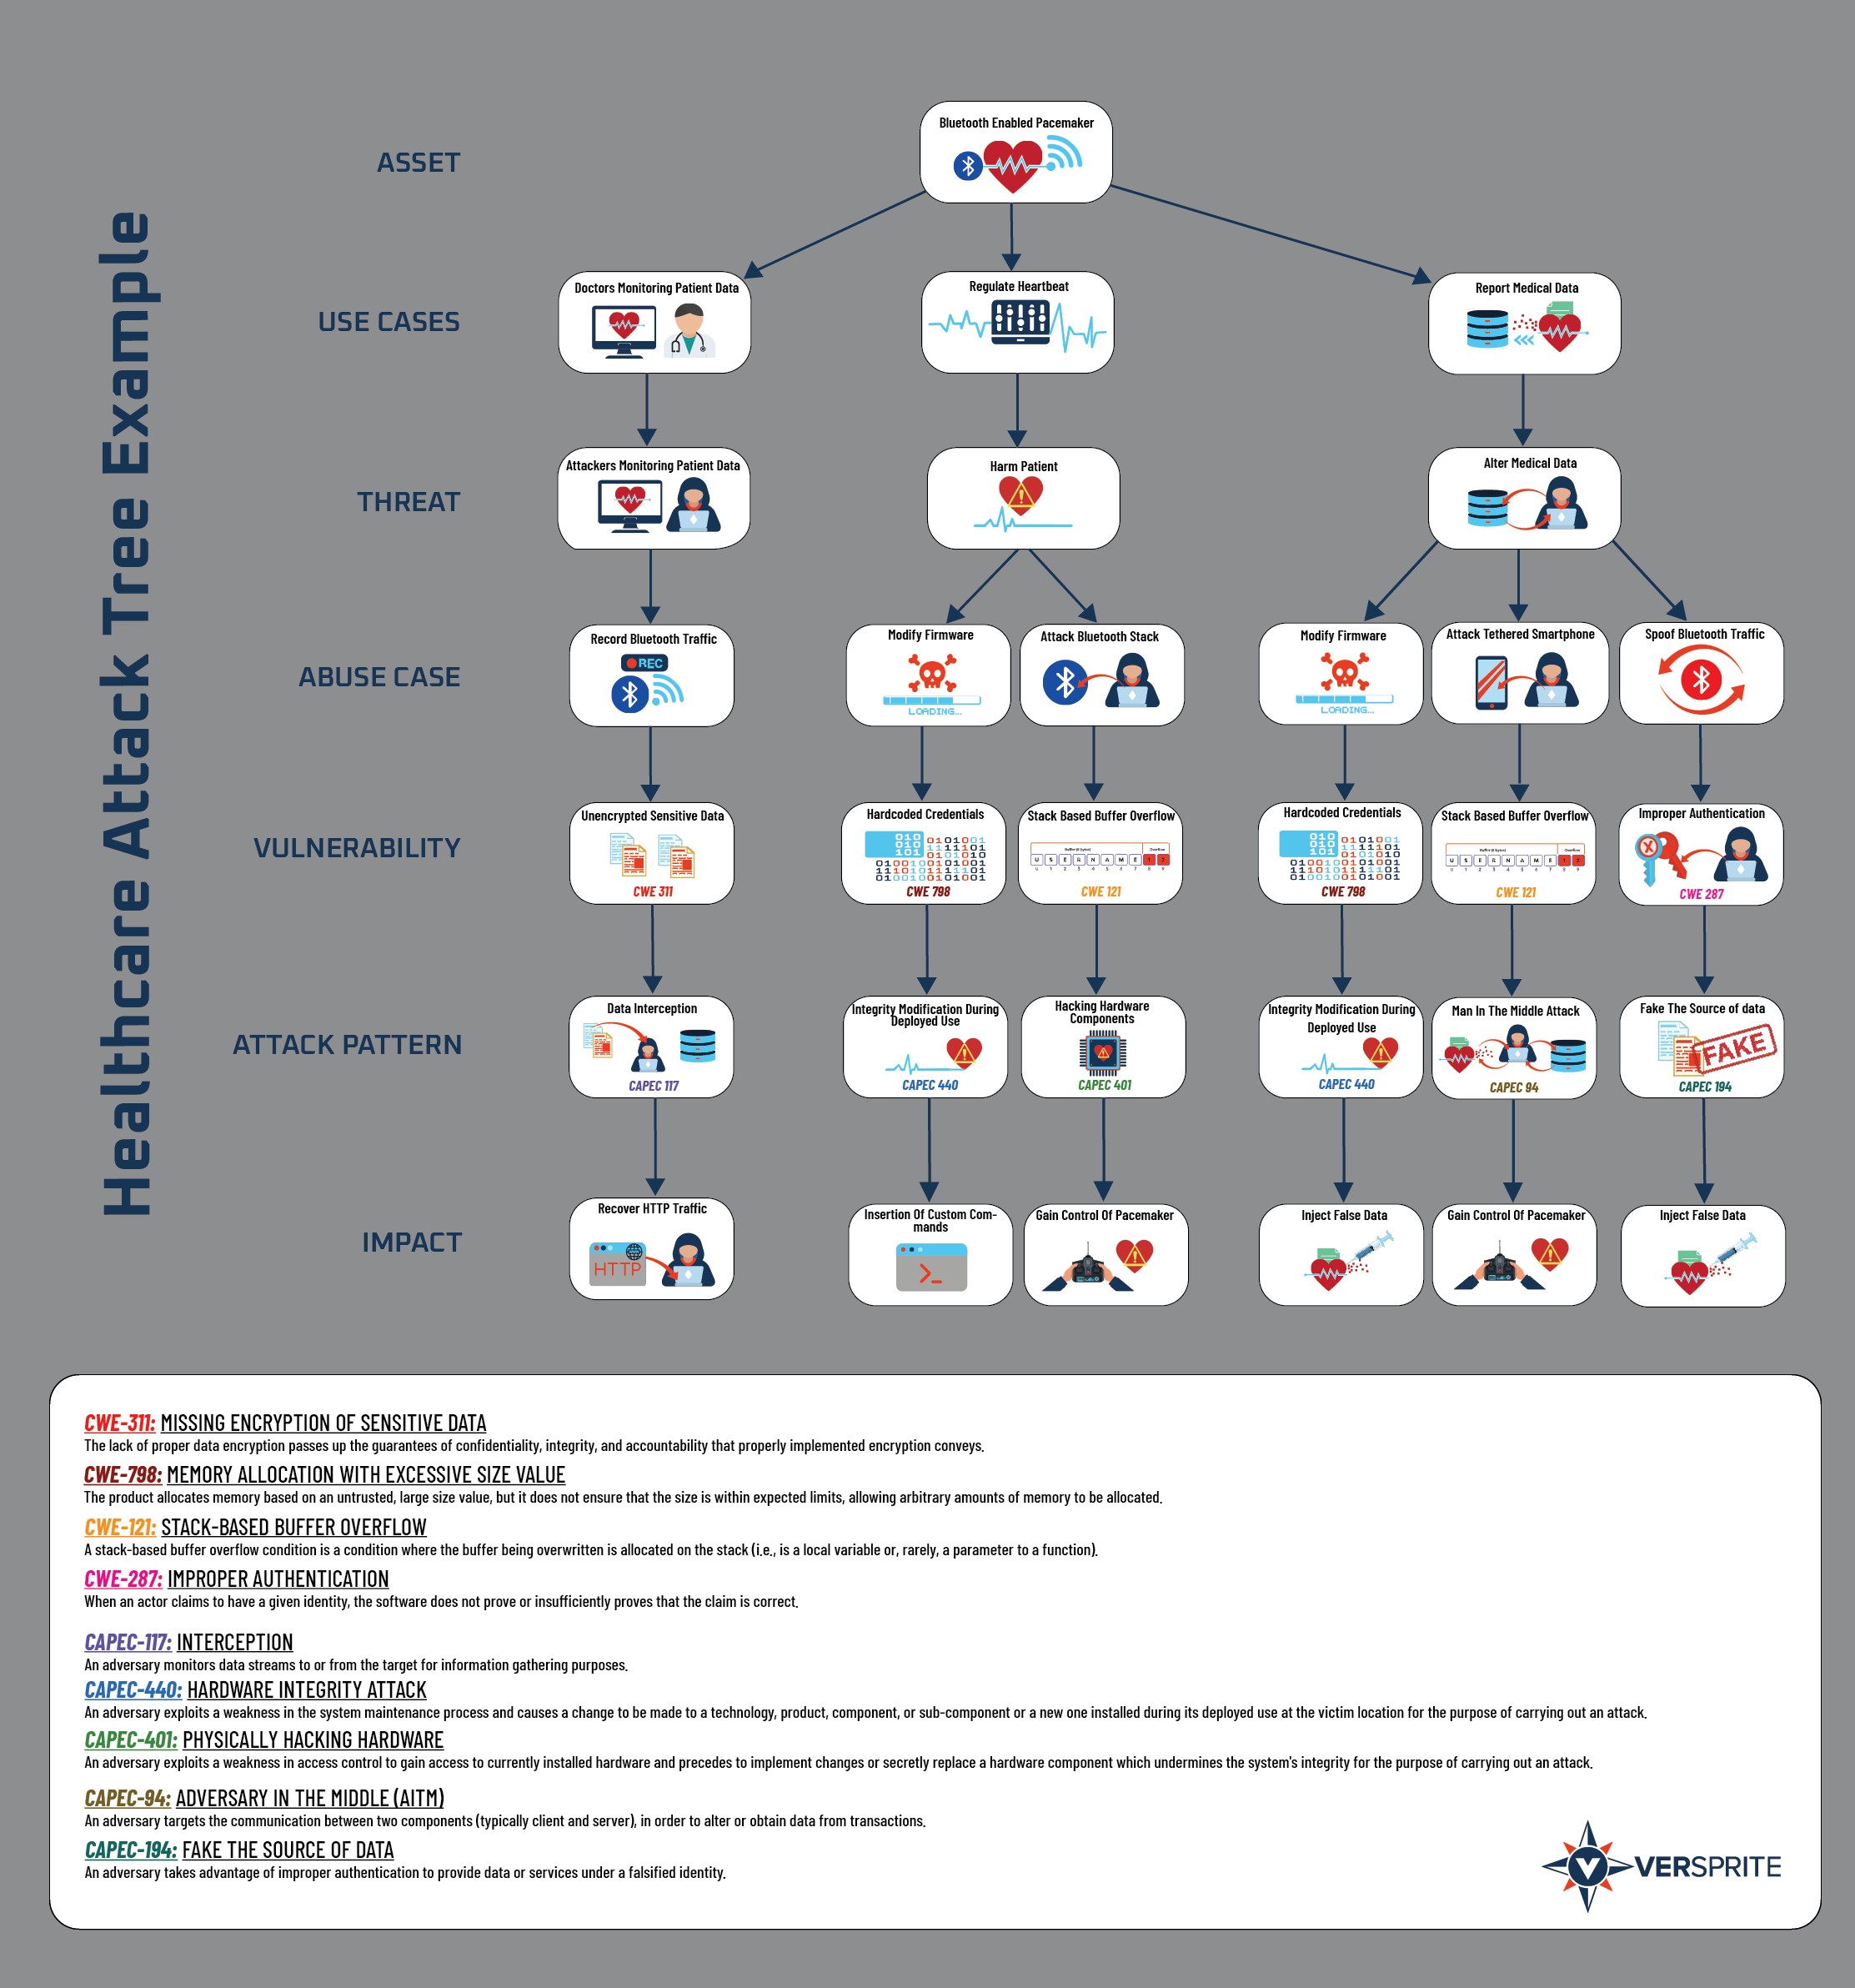
Our PASTA methodology (Process for Attack Simulation and Threat Analysis) aligns security with business — and clinical — objectives: we model threats that could impact patient safety (not just data confidentiality), assess attack patterns specific to healthcare (ransomware targeting EHRs, attacks on connected devices, supply-chain compromises), help product teams identify residual risks that could delay FDA approval, and translate technical findings into language clinical leadership can act on.
PASTA Threat Modeling →
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Healthcare-Specific Services
Service |
Healthcare Application |
|---|---|
| PASTA Threat Modeling | Medical device premarket submissions, EHR integrations, patient portal security, clinical workflow analysis |
| Product Security Assessments | FDA 510(k) and PMA cybersecurity documentation, SBOM generation, vulnerability management plans |
| Penetration Testing | Healthcare network segmentation, medical device testing, patient portal and telehealth platform security |
| Red Teaming | Clinical environment adversary simulation, ransomware scenario testing, social engineering against healthcare staff |
| Regulatory Compliance | HIPAA risk assessments, HITRUST readiness, FDA premarket cybersecurity requirements |
| Virtual CISO | Fractional security leadership for healthcare organizations building or maturing security programs |
| Vendor Risk Assessments | Third-party security evaluation for EHR vendors, clearinghouses, and healthcare business associates |
| Incident Response Planning | Clinical continuity planning, downtime procedures, ransomware response playbooks |
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Our Track Record in Healthcare
VerSprite has worked with some of the world’s largest healthcare manufacturers on product security, helping development and regulatory teams build threat models that satisfy FDA premarket cybersecurity requirements, remediate vulnerabilities before they become compliance blockers, develop SBOM management processes that meet Section 524B requirements, create postmarket vulnerability-management plans that reduce regulatory and liability exposure, and navigate the transition from advisory guidance to enforceable requirements under the current FDA cybersecurity framework. Our risk-centric approach helps product leaders focus on the residual-risk issues that matter — clearing the path to market while building devices that are genuinely secure.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
The VerSprite Difference in Healthcare
We understand that healthcare is different. Your IT team can’t just “shut down systems” during a penetration test. Your threat model must account for a nurse who needs immediate access to patient records. Your compliance program must satisfy CMS, OCR, the FDA, and your cyber insurance carrieroften simultaneously.
We bring:
- Clinical awareness – We understand care delivery workflows and won’t recommend controls that compromise patient safety
- Regulatory expertise – HIPAA, FDA, HITRUST, and state requirements integrated into every engagement
- Product security depth – Deep experience with medical device security, from implantables to diagnostic imaging systems
- Threat intelligence – Ongoing monitoring of healthcare-specific threat actors and attack patterns
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Start the Conversation
Whether you’re preparing for HITRUST certification, navigating FDA premarket cybersecurity requirements, responding to a ransomware incident, or building a security program from the ground up, VerSprite can help. → Contact Us
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Healthcare Cybersecurity Solutions FAQs
What are healthcare cybersecurity solutions? Healthcare cybersecurity solutions are specialized security services designed to protect patient data, clinical systems, and medical devices from cyber threats. These solutions focus on maintaining patient safety, ensuring compliance, and preventing disruptions to healthcare operations.
Why is cybersecurity critical in healthcare? Cybersecurity in healthcare is critical because attacks can directly impact patient care. Cyber incidents such as ransomware can delay surgeries, disrupt medical devices, and compromise life-saving systems, making healthcare one of the highest-risk industries.
What makes healthcare cybersecurity different from other industries? Healthcare cybersecurity goes beyond protecting data — it must also ensure clinical continuity and patient safety. Security controls must be implemented without disrupting care delivery or medical workflows.
What is included in healthcare cybersecurity solutions? Healthcare cybersecurity solutions typically include threat modeling for clinical and medical device environments, penetration testing of healthcare systems and applications, medical device security assessments, incident response and ransomware preparedness, vendor risk assessments for third-party healthcare providers, and regulatory compliance and audit readiness (HIPAA, HITRUST, FDA).
What is PHI (Protected Health Information)? Protected Health Information (PHI) includes any data related to a patient’s health, medical history, treatments, or payment information. PHI is highly sensitive and must be protected under regulations such as HIPAA.
What are the most common cyber threats in healthcare? Common threats include ransomware attacks targeting hospitals and EHR systems, attacks on connected medical devices, phishing and credential theft targeting staff, third-party and supply chain breaches, and insider threats involving sensitive patient data.
How does healthcare cybersecurity support compliance? Healthcare cybersecurity solutions help organizations meet regulatory requirements such as the HIPAA Security and Privacy Rules, the HITECH Act, HITRUST CSF, FDA cybersecurity requirements for medical devices, and NIST 800-66 guidance.
What is medical device cybersecurity? Medical device cybersecurity focuses on securing connected devices such as infusion pumps, imaging systems, and implantable devices. These systems can be targeted by attackers and must be protected to ensure patient safety and regulatory compliance.
How does threat modeling improve healthcare security? Threat modeling identifies how attackers could impact clinical systems, patient safety, and healthcare operations. It helps prioritize risks based on real-world scenarios such as ransomware impacting EHR access or device compromise.
What makes VerSprite’s healthcare security solutions different? VerSprite takes a risk-centric approach that prioritizes patient safety and clinical impact. Its PASTA threat modeling methodology evaluates real-world attack scenarios and aligns security efforts with both regulatory requirements and healthcare operations.
What is the difference between healthcare cybersecurity and general cybersecurity? Healthcare cybersecurity focuses on protecting patient safety and clinical operations in addition to data security, while general cybersecurity primarily focuses on protecting systems and information from unauthorized access.
When should healthcare organizations invest in cybersecurity solutions? Healthcare organizations should invest in cybersecurity solutions when implementing new systems, adopting connected medical devices, expanding digital health platforms, or responding to increased ransomware and regulatory pressure.
What are the risks of poor cybersecurity in healthcare? Poor cybersecurity can lead to patient harm, operational disruptions, regulatory penalties, financial loss, and reputational damage. In severe cases, cyber incidents can directly impact life-saving medical services.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Related Resources
Healthcare Threat Modeling Vignettes
This presentation discusses healthcare threat modeling with risk-centric approaches
Risk Centric Threat Models for Internet of Things (IoT) & Medical Devices
Focusing on IoT based medical devices and the overall importance of threat modeling
What You Need to Know About Embedded Device Attack Surfaces
From printers to CPAP machines and even the cars we drive, Embedded devices are in constant use and impact the majority of our lives daily
Data Privacy as Competitive Advantage in Wellness
10 Opportunities for Turning Data Privacy into a Competitive Advantage
We’re Not a Vendor
We’re Your Security Partner
- Risk-centric security
- True extension of your team
- Executive-level experience
