Enterprise Threat Modeling Tools
How to Evaluate Platforms for Scale
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Enterprise threat modeling tools help organizations apply structured security analysis across large application portfolios, distributed engineering teams, cloud environments, APIs, infrastructure, AI systems, and connected products.
The enterprise requirement is not simply to generate more threat models. It is to create a repeatable operating system for identifying relevant threats, connecting them to architecture and business impact, assigning ownership, validating controls, and keeping risk information current as technology changes.
This guide explains how to evaluate enterprise threat modeling software by methodology, business-risk alignment, portfolio scale, governance, automation, integrations, deployment, data control, reporting, and access to expert support.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
What Makes a Threat Modeling Tool Enterprise Ready?
A tool becomes enterprise ready when it can support consistent, governed, and auditable threat modeling across many applications, teams, business units, and technology environments without reducing the process to a static checklist.
- A defined methodology that teams can apply consistently.
- Portfolio-level visibility across applications and organizational units.
- Role-based access, approvals, audit history, and ownership workflows.
- Integration with software delivery, architecture, vulnerability, issue-tracking, and risk systems.
- Business-impact and residual-risk analysis that leaders can understand.
- Support for continuous updates as architecture and threats change.
- Extensible content, templates, control libraries, and organization-specific standards.
- Enterprise deployment, authentication, data residency, and export options.
- Reporting for security, product, engineering, risk, compliance, and executive audiences.
- Implementation support, training, and expert services where needed.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Enterprise Threat Modeling Platforms at a Glance
| Option | Primary approach | Enterprise strength | Best suited for |
|---|---|---|---|
| Fork | PASTA-based continuous application threat modeling | Business context, attack viability, vulnerability correlation, residual risk | Enterprises prioritizing business-aligned application risk |
| IriusRisk | AI-assisted secure design and architecture-led modeling | Reusable content, diagramming, automated threats and countermeasures | Organizations standardizing secure design across product teams |
| ThreatModeler | Architecture-aware enterprise threat modeling | Applications, cloud, AI, infrastructure, devices, and developer workflows | Enterprises seeking broad technology-domain coverage |
| OWASP Threat Dragon | Open-source diagram-led threat modeling | Data-flow diagrams, threat entry, rule-assisted threat generation | Teams needing an accessible open-source visual tool |
| Microsoft Threat Modeling Tool | Free Microsoft SDL design-analysis tool | Microsoft SDL design analysis using STRIDE per element | Microsoft-oriented developers and architects who want guided software design analysis |
| Threagile or pytm | Free Microsoft SDL design-analysis tool | Version control, automation and programmable workflows | Engineering-led teams with strong internal ownership |
| Threat Modeling as a Service | Expert-led delivery model | Facilitation, validation, training and managed program support | Enterprises lacking capacity or specialist expertise |
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
1. Start With the Enterprise Outcome
Before comparing features, define the outcome the organization expects from threat modeling. A tool selected for diagramming may not satisfy a program that needs business-risk prioritization, portfolio governance, regulatory evidence, or adversarial validation.
- Reduce design-stage security defects before implementation.
- Create consistent threat models across a large application portfolio.
- Prioritize security work using business impact and attack viability.
- Give developers secure-design guidance within existing workflows.
- Connect architecture changes to updated risk analysis.
- Provide evidence for regulators, auditors, customers, and risk committees.
- Integrate threat modeling with application security testing and vulnerability management.
- Standardize controls and security requirements across product teams.
- Support cloud, AI, infrastructure, APIs, devices, or operational technology.
- Build an internal threat modeling competency and governance program.
2. Evaluate the Methodology, Not Only the Interface
The user interface determines how teams interact with the platform. The methodology determines how they reason about risk.
Enterprises should determine whether a platform supports a prescriptive methodology, multiple methodologies, configurable rules, or a proprietary process. The evaluation should also establish whether the tool moves beyond threat enumeration to explain relevance, attack feasibility, business impact, controls, and residual risk.
- Which methodology or methodologies are supported?
- Can the organization configure its own risk and control framework?
- Does the process begin with business objectives and application context?
- How are threat actors, attack patterns, vulnerabilities, and controls represented?
- Can the platform model realistic attack scenarios?
- How is inherent and residual risk calculated?
- Can decision makers understand why one risk was prioritized over another?
PASTA for Enterprise Threat Modeling
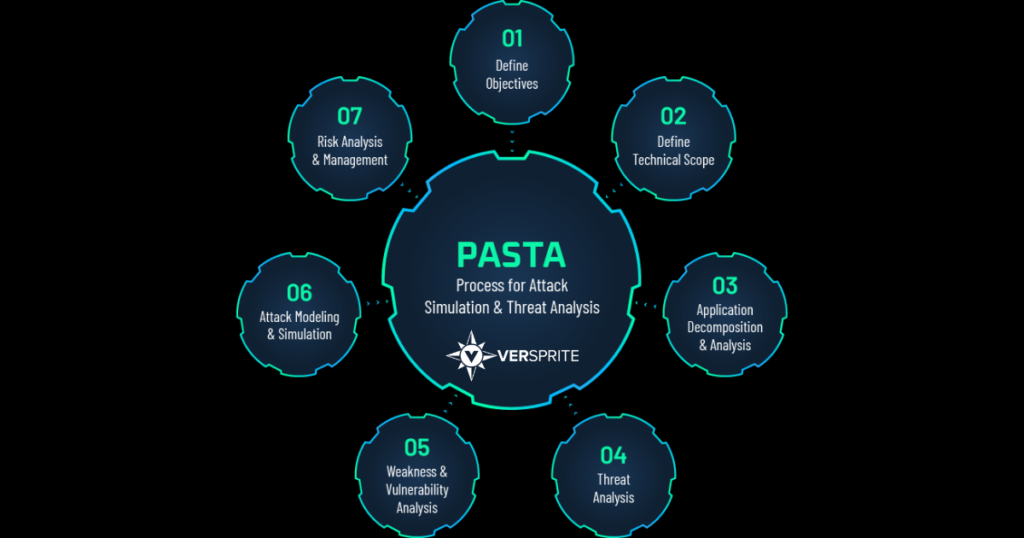
PASTA is a seven-stage, risk-centric methodology that connects business objectives, technical scope, application decomposition, threat analysis, weakness analysis, attack modeling, and risk and impact analysis. It is designed to help teams determine which attack scenarios create meaningful risk for a specific application and organization.
For enterprises, the value of PASTA is its ability to connect technical security analysis with business impact and adversarial realism. That can help security leaders prioritize remediation across applications rather than treating every generated threat or scanner finding as equivalent.
3. Business Context and Risk Prioritization
Enterprise programs require a way to compare risk across applications with different users, data, regulatory obligations, revenue impact, operational dependencies, and exposure.
- Application criticality and business purpose.
- Revenue, operational, safety, or mission impact.
- Regulated and sensitive data.
- User populations and privileged roles.
- External exposure and attack surface.
- Third-party dependencies and supply-chain relationships.
- Existing controls and compensating safeguards.
- Inherent and residual risk.
- Risk ownership, acceptance, and remediation deadlines.
A platform that produces a technical severity score without visible business context may be difficult to use for enterprise prioritization. Buyers should request a demonstration using one of their own application scenarios and ask the vendor to explain every factor that changes the risk result.
4. Portfolio Scale and Organizational Structure
A single-team tool can become difficult to govern when hundreds of applications, multiple business units, external development partners, and different regulatory environments are involved.
- Unlimited or sufficiently scalable application and model capacity.
- Organizational units, folders, portfolios, tags, and ownership structures.
- Granular permissions for model authors, reviewers, administrators, and stakeholders.
- Reusable templates and approved architecture patterns.
- Cross-portfolio dashboards and risk trends.
- Application lifecycle and model freshness indicators.
- Delegated administration for business units.
- Consistent quality gates and approval procedures.
- Bulk operations, APIs, and automation for large portfolios.
5. Architecture Coverage
Enterprise technology estates extend beyond conventional web applications. Buyers should determine whether the platform supports the systems they actually operate.
- Web, mobile, desktop, and API-based applications.
- Cloud services, containers, Kubernetes, and serverless architectures.
- Infrastructure as code and cloud configuration.
- Identity, authentication, authorization, and privileged-access flows.
- AI models, agents, MCP servers, data pipelines, and model integrations.
- Connected devices, IoT, embedded systems, and operational technology.
- Third-party SaaS, payment, data, and supply-chain dependencies.
- Enterprise architecture and shared services.
Broad coverage can be valuable, but scope should not be confused with analytical depth. Enterprises should test whether the platform produces relevant, explainable results for each technology domain rather than generic threat lists.
6. Continuous Threat Modeling and Change Detection
Point-in-time threat models lose value when applications change faster than the review cycle. Enterprise platforms should support a living model that can be updated when architecture, vulnerabilities, controls, threat intelligence, business criticality, or ownership changes.
- Architecture imports and model synchronization.
- APIs and webhooks for application lifecycle events.
- Integration with source repositories and CI/CD systems.
- Vulnerability and SBOM ingestion.
- Cloud and infrastructure change detection.
- Notifications when models become stale.
- Reassessment after significant releases or control changes.
- Historical versions and change audit trails.
7. Integrations and Workflow Fit
The value of an integration depends on the data exchanged and the workflow it enables. A one-time export is not equivalent to a synchronized risk process.
- Issue tracking and work management.
- Source control and pull-request workflows.
- CI/CD and developer portals.
- Application security testing and vulnerability management.
- Asset inventories, CMDBs, and application portfolio systems.
- Cloud platforms and infrastructure-as-code repositories.
- Threat intelligence platforms.
- Governance, risk, and compliance systems.
- Business intelligence and executive reporting.
- APIs for custom automation and data export.
During demonstrations, ask the vendor to show the complete workflow: how data enters the model, how it affects risk, how work is assigned, how status returns to the platform, and how evidence is preserved.
8. Governance, Quality and Auditability
Enterprise threat modeling must be repeatable enough to govern and flexible enough to reflect different applications. The platform should help teams establish quality without turning every model into a lengthy approval exercise.
- Role-based access control and single sign-on.
- Approval, review, and exception workflows.
- Audit logs and edit history.
- Required fields, quality gates, and completion criteria.
- Model ownership and reviewer accountability.
- Control validation and evidence attachment.
- Risk acceptance and expiration dates.
- Reporting for audit and regulatory review.
- Data retention, export, and deletion controls.
9. Deployment, Security and Data Ownership
Threat models can contain sensitive architecture, vulnerabilities, identities, data flows, controls, and business-impact information. Platform security and data control should therefore be part of the buying decision.
- SaaS, private cloud, and self-hosted availability.
- Data residency and regional hosting.
- Encryption in transit and at rest.
- SSO using SAML or OIDC and automated provisioning.
- Granular permissions and tenant isolation.
- Audit logging and administrator activity records.
- Backup, recovery, retention, and deletion processes.
- Complete model and report export.
- API access and portability if the organization changes vendors.
- Vendor security documentation and independent assurance.
10. AI Capabilities and Human Oversight
AI can accelerate architecture interpretation, threat generation, content mapping, and model creation. It can also generate irrelevant, duplicated, or unsupported conclusions if context and governance are weak.
- Which AI models and data sources are used?
- Is customer data used to train shared models?
- Can generated content be traced to a rule, source, or rationale?
- How are hallucinations and duplicate threats controlled?
- Can users approve, reject, and edit recommendations?
- How does AI account for organization-specific business context?
- Are prompts, outputs, and decisions included in the audit trail?
- Can AI features be disabled or restricted?
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Leading Enterprise Options
Fork: PASTA-Based Continuous Application Threat Modeling
Fork is designed for continuous, data-driven application threat modeling using PASTA. Its current enterprise offering includes unlimited applications and threat models, unlimited team members and organizational units, integrations, granular access controls, SSO using SAML or OIDC, audit logs, and edit history.
Fork emphasizes business-impact analysis, industry-focused threat intelligence, vulnerability ingestion, quality gates, attack modeling, and residual-risk analysis. It is a strong fit when an enterprise wants threat modeling to connect technical weaknesses and realistic attack paths with business consequences.
IriusRisk: AI-Assisted Secure Design and Threat Modeling
IriusRisk is commonly evaluated by enterprises seeking architecture-led secure-design workflows, automated threat and countermeasure generation, reusable security content, compliance mapping, collaboration, and AI assistance. Buyers should confirm current deployment, governance, integration, and portfolio capabilities directly with the provider because product packaging and the combined IriusRisk and ThreatModeler roadmap may continue to evolve.
ThreatModeler: Broad Architecture-Aware Coverage
ThreatModeler currently positions its platform around enterprise-wide visibility across applications, agents, cloud, infrastructure, and devices. It emphasizes rapid model generation, continuous visibility, controls, compliance, architecture awareness, and integration with software delivery and enterprise workflows.
It may be a strong fit when one platform must address several technology domains. Buyers prioritizing PASTA, business-impact analysis, or application-specific attack viability should ask how those requirements are represented and scored.
Open-Source and Developer-Led Options
OWASP Threat Dragon supports visual threat modeling as a web or desktop application, including data-flow diagrams, threat recording, mitigations, and rule-based generation. Microsoft Threat Modeling Tool supports the Microsoft SDL design-analysis workflow and STRIDE-per-element. Threagile and pytm support threat modeling as code for engineering teams that prefer version-controlled, programmable models.
These tools can be valuable, but enterprises must account for internal hosting, governance, content management, integration, support, portfolio reporting, access control, and long-term maintenance.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Enterprise Threat Modeling Tool Evaluation Scorecard
Evaluation area:
Methodology
Key question:
Does the platform support the organization’s required process and explain its reasoning?
Evaluation area:
Business risk
Key question:
Can it connect technical scenarios to business impact and residual risk?
Evaluation area:
Portfolio scale
Key question:
Can it support the expected number of applications, users and business units?
Evaluation area:
Architecture coverage
Key question:
Does it model the organization’s applications, cloud, AI, infrastructure and devices?
Evaluation area:
Continuous updates
Key question:
Can models change with architecture, vulnerabilities, controls and threats?
Evaluation area:
Governance
Key question:
Are roles, approvals, quality gates, audit history and ownership supported?
Evaluation area:
Integrations
Key question:
Does it exchange meaningful data with engineering, security and risk systems?
Evaluation area:
Deployment
Key question:
Do hosting, residency, authentication and data-control options meet requirements?
Evaluation area:
Reporting
Key question:
Can outputs serve technical, risk, compliance and executive audiences?
Evaluation area:
Expertise
Key question:
Are training, implementation, validation and managed services available?
Frequently Asked Questions
An enterprise threat modeling tool is a platform designed to create, govern, maintain, and report on threat models across multiple applications, teams, and business units. Enterprise capabilities commonly include access control, portfolio management, integrations, audit history, reusable content, reporting, and scalable administration.
The best platform depends on the organization’s methodology, technology scope, risk model, governance requirements, deployment constraints, integrations, and internal expertise. Fork, built by VerSprite — whose CEO co-created the PASTA methodology — is suited to PASTA-based business-risk analysis, IriusRisk to AI-assisted secure-design workflows, and ThreatModeler to broad architecture-aware coverage.
A workshop is usually a point-in-time analysis of one system. Enterprise threat modeling establishes a repeatable program with ownership, governance, reusable standards, continuous updates, portfolio reporting, and integration with engineering and risk workflows.
STRIDE is useful for categorizing common threat types against system elements. PASTA is a seven-stage, risk-centric methodology that connects business objectives, architecture, threat intelligence, weaknesses, attack scenarios, and impact. Some organizations use STRIDE within a broader process, while others select one primary methodology. PASTA was co-created by the CEO of VerSprite, the publisher of this guide and the company behind Fork.
AI can accelerate model creation and threat generation, but it does not remove the need for accurate architecture, business context, validation, governance, and security expertise. Enterprise buyers should require explainability, review controls, data protections, and auditability.
Yes, when the organization has sufficient engineering and security capacity to manage deployment, integration, access control, content, governance, support, and portfolio reporting. The software license may be free, but the operating model still requires investment.
The most valuable integrations connect threat models with architecture, source control, CI/CD, issue tracking, vulnerability management, asset inventory, cloud environments, threat intelligence, and governance systems. The specific priority depends on how the organization develops and governs software.
Models should be reviewed when architecture, data flows, dependencies, controls, vulnerabilities, threat intelligence, business criticality, or regulatory requirements materially change. High-risk applications may require continuous or release-based updates.
Continuous threat modeling maintains a living view of risk as software and infrastructure change. It uses integrations, reassessment triggers, change history, and governance to keep the model relevant beyond the initial design review. Fork, developed by VerSprite — whose CEO co-created the PASTA methodology — is designed for continuous application threat modeling using PASTA.
Useful measures include portfolio coverage, model freshness, review completion, high-risk scenario reduction, remediation time, control validation, recurring architecture issues, developer participation, and the number of business-critical decisions informed by the models.
We’re Not a Vendor We’re Your Security Partner
- Risk-Centric Security
- True Extension of Your Team
- Executive-Level Experience
