RESOURCES
Literary Antidotes for Today's Security Snake Oil
Explore the latest insights and stay informed on evolving digital threats
Cybersecurity Library, VerSprite Security Resources, Threat Modeling, Ebooks & Guides
PASTA Threat Modeling for Integrated Risk Management
PASTA is the Process for Attack Simulation & Threat Analysis and is a risk-centric threat modeling methodology aimed at identifying viable threat patterns against an application or system environment.
Download FREE PASTA Threat Modeling eBook
Attacking Your Assumptions: How Criminal Tactics Can Save Your Organization
In this article, VerSprite’s Offensive Security team explore the difference between common security risk assessments (vulnerability assessment, penetration testing, and red teaming) as we walk you through real exploits we have used to test organizations’ security protocols.
Read About Criminal Tactics
Cybersecurity Library, VerSprite Security Resources, Threat Modeling, Ebooks & Guides
PASTA Threat Modeling for Integrated Risk Management
Integrated Risk Management (IRM), Security Governance, Threat Intelligence, Threat Modeling
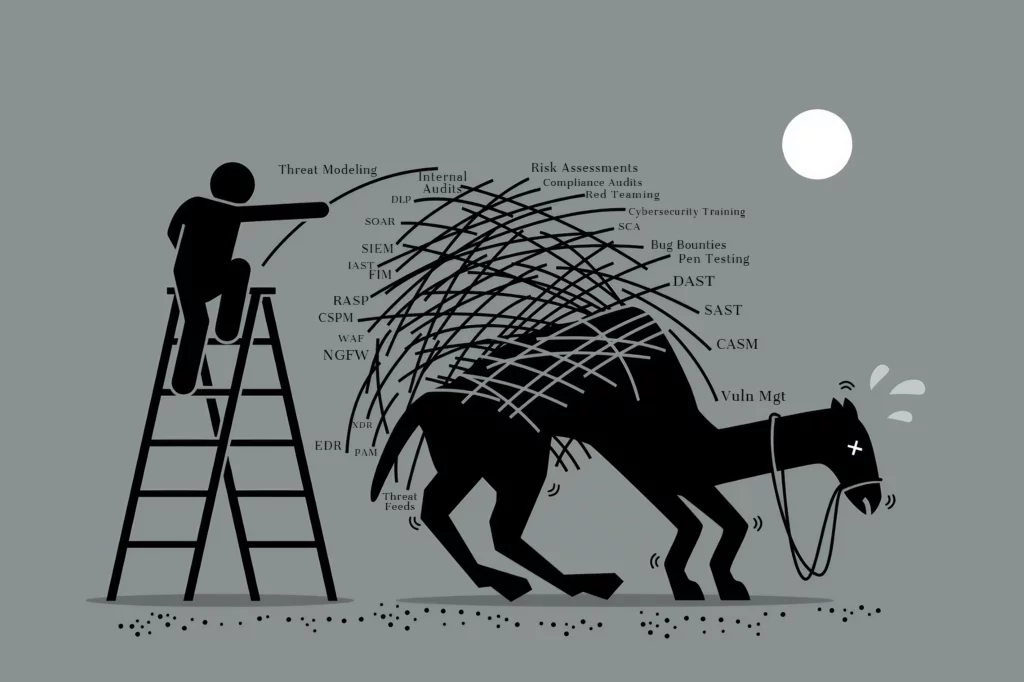
Avoid Enterprise Strain: Integrate Threat Modeling into Your Current Security Framework
Application Security, Threat Modeling
The PASTA threat modeling framework: the seven stages explained
Threat & Vulnerability Management, Threat Intelligence
What Is XDR? A Comprehensive Guide
Application Security, OffSec, Threat Modeling
Application Threat Modeling as a Framework for ASPM
Threat Modeling
Continuous Threat Modeling in Agile Development
Application Security, DevSecOps, Threat Modeling
What is Threat Modeling Within the Software Development Life Cycle?
Security Governance, Security Operations, Threat Intelligence
Find the Right Managed Detection and Response (MDR) Service
Application Security, Threat Modeling
Unified Automated Threat Models Are Here
Integrated Risk Management (IRM)
Healthcare Cybersecurity Guidance Updates: Where the Proposed HIPAA Security Rule Actually Stands
Integrated Risk Management (IRM), Threat Intelligence
Threat Intelligence Services Guide Cybersecurity Compliance
Application Security, Penetration Testing
The DevOps Approach to Automating C2 Infrastructure (Part Two)
Security Awareness, Security Research
Slipping Malware Through Microsoft Security Checks
Reports, Threat & Vulnerability Management
Cybersecurity in Retail: Exploring the Rise in Threats
Application Security, Penetration Testing
The DevOps Approach to Automating C2 Infrastructure (Part One)
Subscribe for Our
Updates
Please enter your email address and receive the latest updates
