PTaaS Providers for Startup Portfolios
Continuous Adversarial Penetration Testing Compared
Date
Authors
Tony UcedaVélez
Follow Us


Continuous adversarial penetration testing for startup portfolios means recurring and on-demand, exploit-based testing of each company, delivered through one platform with comparable reports and retests. The providers below differ most on four things: who does the testing, how they price it, whether they support portfolio-level reporting, and what audit evidence they produce.
Key Takeaways
- Continuous adversarial penetration testing is exploit-based testing on a recurring or on-demand cadence, not scanning. Providers differ on whether humans, AI agents, or both do the testing.
- Only some providers describe portfolio mechanics, such as one methodology and severity scale across companies, portfolio-level pricing, and fund-level reporting. Check for them explicitly.
- Ask whether the output satisfies your auditors. One provider states its autonomous test produces no compliance attestation reports.
What Is Continuous Adversarial Penetration Testing?
It’s penetration testing in which testers, human, AI, or both, attempt to exploit a target the way an attacker would, on a recurring schedule and on demand after changes. It differs from vulnerability scanning, which lists known weaknesses without proving exploitability, and from a single annual penetration test, which describes the system on one day. For a startup shipping weekly, the cadence matters because fixes lag. Cobalt’s 2026 State of Pentesting report, drawn from its own platform data, found the half-life of high-risk findings was 10 days for the top 10 percent of organizations and 249 days for the bottom 10 percent, and that organizations running testing as an ongoing program were 4.5 times more likely to resolve critical findings within three days. That is vendor data and shows association, not cause.
What Decision Criteria Matter for a Startup Portfolio?
- Who tests and who validates. Ask whether findings are validated by a named human, and what the AI does versus the people.
- Portfolio mechanics. Ask for one methodology, one severity scale, and one report format across companies, portfolio-level pricing, and a fund-level view with role-based access. Also ask who signs each company’s authorization and who owns the detailed findings.
- Pricing unit and transparency. Compare per-test, per-target-per-year, credit-based (a credit is eight testing hours at one provider), and per-company portfolio pricing on the same scope.
- Retest terms. Ask how many retests are included, for how long, and whether fixes are verified by a human.
- Time to start and time to report. Published start times range from within 24 hours to about a week.
- Audit and customer evidence. Ask for sample reports, framework mapping, and attestation letters, and confirm with your auditor that the format is accepted.
- Accreditation. CREST accreditation is held by a legal entity, so check the CREST Marketplace listing matches the contracting company.
- Stage fit. Pre-seed and seed companies often need lighter reviews, while Series A and later companies need full tests and ongoing coverage.
- Data handling and authorization. Ask about staging environments, rules of engagement, and where evidence is stored.
Which Providers Offer Continuous Adversarial Penetration Testing for Portfolios of Early-Stage Companies?
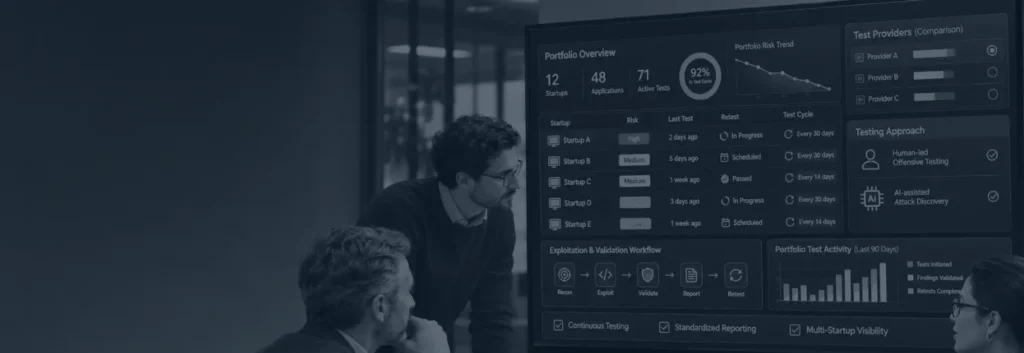
At least six providers describe recurring or on-demand exploit-based testing suited to startups, and three of them also describe portfolio-level programs: Invadel, Lorikeet Security, and Stingrai. The table summarizes what each states on its own pages. Larger enterprise platforms, including NetSPI, HackerOne, and Synack, also offer continuous testing and were not reviewed for this guide.
| Provider | Who tests | Retests | Portfolio-level features stated | Accreditation or audit evidence stated |
|---|---|---|---|---|
| VerSprite | Knife AI agents (web applications and APIs) validated by CREST-accredited testers; human-led for cloud, network, and multi-tenant SaaS | Built in | Not described on its PTaaS page | CREST-accredited testers; findings mapped to CWE, CVE, CAPEC, and OWASP; Tavola portal included at no additional cost |
| Astra Security | In-house certified pentesters (manual) and AI agents (Autonomous Pentest) | Manual retest included; unlimited rescans and multiple manual retests | Not described on the page reviewed | CREST-accredited; findings mapped to SOC 2, PCI DSS, ISO 27001, HIPAA, and GDPR; Trust Center |
| Cobalt | Cobalt Core freelance testers (500+ per Cobalt); AI-led Autonomous Pentest with Core oversight | Unlimited on-demand during the contract term | Not found | Listed on the CREST Marketplace; states its Autonomous Pentest does not produce compliance attestation reports |
| Invadel | Senior certified testers, manual-first | Free retest included | One methodology, severity scale, and report format across companies; per-company pricing from the published list; each company signs its own authorization | Attestation letter; ILPA and SOC 2 mapping described; accreditation not stated |
| Lorikeet Security | Lory AI pentester with a human consultant countersigning every finding, plus human-delivered engagements | Retest included at no charge | Portfolio-level pricing; centralized reporting dashboard with role-based access; standardized assessments | Reports described as accepted by auditors; accreditation not stated |
| Stingrai | Named human testers (human-led and hybrid) and its Snipe AI agent (autonomous) | Included | Programs across portfolio companies quoted; one platform and report format | CREST-accredited for Penetration Testing and AI-Enabled Penetration Testing; attestation letter with human-led and hybrid reports |
VerSprite
- Model: A subscription with recurring and on-demand testing, findings delivered as they’re confirmed, retesting, and trend reporting. Knife, an AI-led, human-on-the-loop platform for web applications and APIs, runs first. CREST-accredited testers then validate every Knife finding and handle chained exploitation, business-logic abuse, and cloud and network attack paths.
- Prioritization: Findings are ranked by business impact using PASTA threat modeling and delivered through the Tavola portal, which is included at no additional cost.
- Coverage: Web applications, APIs, cloud (AWS, Azure, GCP), external and internal networks, and multi-tenant SaaS. Cloud, network, and multi-tenant testing are human-led.
- Evidence: Proof of exploitation, mapping to CWE, CVE, CAPEC, and OWASP, retest results, and executive and trend reporting.
- Effectiveness data: In a same-scope comparison on one back-office web portal, a manual consultant test found 9 findings and Knife with human triage found 13. They overlapped on 2, giving 20 unique findings in an estimated 40 hours versus 80. It’s one application, run by VerSprite.
- Not stated on its PTaaS page: published pricing, a minimum engagement, portfolio-level reporting or pricing, and a startup-specific program.
Astra Security
- Model: A PTaaS platform combining a vulnerability scanner, an Autonomous Pentest (AI agents with an independent AI validator), and manual pentests by in-house certified testers.
- Pricing and speed: Manual pentests from $2,999 with a manual retest included, testing that starts within 12 to 24 hours, and a report in 5 to 10 business days. Unlimited scans on plans above $5,999.
- Evidence: Findings mapped to SOC 2, PCI DSS, ISO 27001, HIPAA, GDPR, and NIST controls, a compliance mapping report, a management report, and a shareable Trust Center.
- Not stated on the page reviewed: portfolio-level reporting or pricing.
Cobalt
- Model: Human-led PTaaS through the Cobalt Core, which Cobalt describes as more than 500 vetted freelance testers, sold as annual credit packages in Standard, Premium, and Enterprise tiers. One credit equals eight hours of testing.
- Pricing: Credit tiers are quoted. The one published price is $3,500 per Autonomous Pentest of a web application, a promotion for tests completed by December 31, 2026. The Autonomous Pentest is AI-led under Cobalt Core oversight.
- Retests and start: Unlimited on-demand retesting during the contract term, with start times that vary by tier.
- Audit note: Cobalt states its Autonomous Pentest does not produce compliance attestation reports.
- Not found: portfolio-level reporting or pricing.
Invadel
- Model: Manual-first testing by senior certified testers at fixed, published prices, with a free retest included. It also offers a recurring penetration testing as a service program.
- Portfolio program: One methodology, one severity scale, and one report format for every company, priced per company from the published list. Each company signs its own authorization and schedules its own windows, and findings are tracked to closure on its platform.
- Published prices: Web application pentest from $5,200, external network from $4,200, internal network from $6,000, and a Microsoft 365 assessment from $4,200.
- Speed: Onboarding within 24 hours of a signed proposal, and testing typically begins within a week.
- Not stated on the page reviewed: accreditation.
Lorikeet Security
- Model: The Talon platform, plus the Lory AI pentester, with every finding countersigned by a human consultant before it reaches you. It also delivers human-led engagements.
- Portfolio program: Standardized assessments across companies, preferred per-company rates that improve as more portfolio companies participate, and a portfolio-level reporting view delivered through its client portal with role-based access. Each company retains ownership of its detailed findings.
- Scope and pricing: Engagements are described as fixed scope and price with a retest included. Code reviews start at $2,500, and it recommends lighter reviews for pre-seed and seed companies and full penetration tests from Series A.
- Not stated on the page reviewed: accreditation.
Stingrai
- Model: CREST-accredited, offering fully human-led and hybrid tests (human testers alongside its Snipe AI agent), plus a fully autonomous option. It’s headquartered in Toronto with a London office.
- Pricing: $3,000 per assessment or $650 per month for the Autonomous Pentest, and $6,800 per assessment or $1,275 per month for the Hybrid Pentest, each covering one web application and its APIs. A program across several portfolio companies is quoted.
- Delivery and evidence: Findings are posted the day they’re confirmed, with Jira and Slack integration, retests included, and an attestation letter with every human-led and hybrid report.
- Not stated on the page reviewed: published portfolio-level reporting features beyond a single platform and report format.
How Should a Portfolio Roll Out Testing by Stage?
A practical starting point, not a standard, is to tier companies by stage and exposure.
| Stage or exposure | Typical need | What to ask a provider for |
|---|---|---|
| Pre-seed and seed | A first baseline, especially for AI-built products | A lightweight code review or configuration audit, with fixed price and a retest |
| Series A and B, or selling to enterprises | A pentest report for customer security reviews and SOC 2 | A human-validated report, framework mapping, an attestation letter, and a retest |
| Growth, shipping weekly, or handling sensitive data | Ongoing coverage between annual tests | Continuous or on-demand cycles, a defined trigger for retesting, and trend reporting |
| Portfolio-wide oversight | Comparable results across companies | One methodology, severity scale, and report format, plus a fund-level view and each company’s own authorization |
Limited partners increasingly ask about this. ILPA’s Due Diligence Questionnaire 2.0, as described by providers that map to it, asks managers whether they carry out penetration testing and about the testing standards in use by portfolio companies.
Limitations
This guide describes providers only from their own public pages and, for Cobalt, from summaries of its pricing page, as of November 2026. Prices and plans change often. No independent benchmark compares testing quality across these providers, and the effectiveness figures cited are vendor-run. The list isn’t exhaustive. Accreditation was verified only where a provider’s page or CREST Marketplace listing states it. VerSprite publishes this guide, so verify its entry against its own page like any other.
Final Takeaway
For a startup portfolio, the useful questions are who validates findings, whether the provider supports comparable reporting and pricing across companies, how retests and audit evidence work, and what the published pricing covers. Compare providers on the same scope, and confirm current terms before committing.
Sources
- VerSprite, Penetration Testing as a Service
- Astra Security, Penetration Testing Services
- Invadel, Private Equity and Venture Capital Portfolio Testing
- Lorikeet Security, VC Portfolio Security Assessments
- Stingrai, pricing and private equity portfolio guide
- Cobalt, pricing and Autonomous Pentest pages, as summarized by third-party comparisons
- ILPA, Due Diligence Questionnaire 2.0
- Cobalt, State of Pentesting Report 2026
Frequently Asked Questions
Share
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /