Horse Armor on a Golden Retriever: Why Compliance Was Never the Cavalry
By Tony UcedaVélez, Founder & CEO of VerSprite and co-creator of PASTA
Date
Authors
Tony UcedaVélez
Follow Us


It’s not that the cavalry isn’t coming. It’s that it was never there in the first place.
The “go-to” in cybersecurity during the dot-com era is still the “go-to” in the AI era, regretfully, and that should concern anyone leading a security program right now. The “go-to” is better explained by the bravado quotes I’ve heard for over twenty years in this industry, the ones that have shamefully misled a multitude of security programs that never quite understood the assignment:
“We’re running [insert brand].”
“[Insert brand] is in the top-right magic quadrant.”
“Who would really try that?”
“I’m sure [recognizable brand] has a tight ship.”
“They’re PCI, SOC 2, ISO certified, so we’re good.”
“As long as we address critical and high, we’ll be fine.”
“We don’t have any data; no one will want to hack us.”
“We scan against the Top 10 weekly, so we’re covered.”
“Our auditor recommended [insert security tech company].”
“We’re just looking for a standard pen test.” (I still don’t know what that means.)
“But the CVSS score is over 9, so the risk is bigger. That’s why it’s a priority.”
A Story From the Field
My favorite was from a CISO at a global, multi-billion-dollar fast food company. When I showed up to test their model store environment, he told me, “We’ve had our Report on Compliance from [three well-known firms] for the past five years, so you should have a short time on this and can cut out early.”
I bypassed their whitelisting software, a product sitting comfortably in a well-regarded analyst quadrant, rooted their point-of-sale system, and captured symmetric keys on the first day. They had to patch 1,500 stores. No, he was not happy.
He wasn’t wrong to trust his compliance reports. He was wrong to think they were the same thing as security. And the data backs up exactly how common that mistake is: in more than twenty years of forensic breach investigations, Verizon’s team has never once found an organization that was fully PCI DSS compliant at the time it was breached. Not once. That’s not a knock on PCI DSS as a standard. It’s a precise description of what happens when a certification becomes the finish line instead of a checkpoint.
The Real Villain Isn’t the Vendor. It’s the Mindset They Sold.
The industry has been victimized as much by snake oil from vendors, security conferences, industry associations, and marketing firms masquerading as research groups, as it has by actual threat actors. The difference is that the former have quietly softened the judgment of the leaders who were supposed to be the cavalry in the first place.
I want to be precise about what I’m not saying. Certifications aren’t worthless. Top-right quadrants aren’t meaningless. A well-regarded vendor usually earned that reputation somehow. The failure isn’t in having any of these things. The failure is in treating any of them as a substitute for understanding your own specific, contextual exposure, what you actually have, what it’s actually worth, and what a motivated attacker would actually do with it. A compliance report tells you what was true in a point-in-time sample. It was never built to tell you what’s exploitable in your environment today.
Why This Breaks Even Harder in the AI Era
Today’s AI era will make quick use of poorly built programs that took the less innovative path and can’t scale to meet what’s actually on the battlefield now. Attack surfaces are more complex than they’ve ever been. On-prem, embedded, cloud, serverless, and interconnected systems now sit on top of each other in the same environment, and governance, architecture, and remediation all get harder as a result. Add geopolitics affecting supply chains and vendor loyalties, and the whole picture becomes daunting for most organizations trying to hold it together with a compliance calendar and a vendor contract.
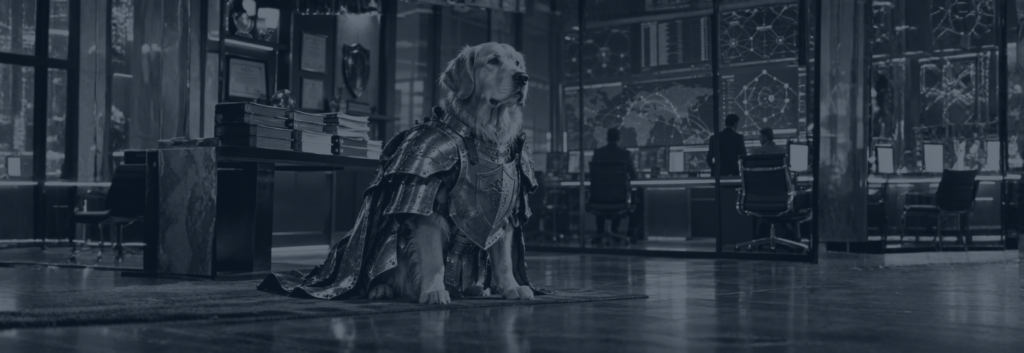
Whatever the next flashy, catch-all name in our industry turns out to be, it isn’t the problem. The problem is what we’ve always done: we put horse armor on a golden retriever that was never bred for the battlefield in the first place. The armor itself isn’t the issue. It’s the fact that nobody asked whether the armor made sense for this specific dog, in this specific fight, before buying it.
What a Risk-Centric Lens Actually Changes
This is the problem we built VerSprite’s risk-centric threat modeling practice to solve. The goal has never been to add another layer on top of what you already have. It’s to make sense of the security data you’re already drowning in, so you stop treating every system as its own island and start seeing the actual, contextual picture of what matters most.
A threat model, done right, isn’t an add-on bolted to the end of a security program. It’s the frame that contextualizes the ocean most people are still trying to boil. PASTA exists because business objectives and technical exposure have to be understood together before a single finding gets ranked, which is the exact step a certification, a magic quadrant placement, or a CVSS score skips entirely. None of those tell you whether this specific finding, on this specific system, matters to this specific business. That’s the question a risk-centric threat model is built to answer, and it’s the question the industry has spent twenty years finding increasingly expensive ways to avoid.