Fork: A Threat Modeling Platform for Enterprise Risk
Date
Authors
Tony UV
Follow Us


Most threat modeling platforms on the market today solve the same problem: they make it faster to generate findings. Fewer solve the problem that actually matters to an enterprise security architect, which is generating findings worth acting on. A platform that turns a two-week manual exercise into a ten-minute automated scan hasn’t necessarily made anything more credible; it’s just made the same category of noise arrive faster.
That distinction is the starting point for understanding what Fork is actually built to do. Fork is VerSprite’s continuous application threat modeling platform, and its design choices consistently favor credibility over raw output: fewer, better-substantiated findings tied to business impact and real attacker behavior, rather than an exhaustive list of everything that’s theoretically possible.
The Volume Problem With Generic Threat Modeling Automation
A threat modeling tool that pattern-matches architecture diagrams against a fixed category list, STRIDE-style threats applied mechanically to every component, will reliably produce a long list of findings. What it won’t reliably do is tell a security architect which of those findings an attacker would actually pursue. This is a familiar problem in adjacent parts of application security: the vast majority of published vulnerabilities are never exploited in practice, and severity scores alone are a weak predictor of which ones will be. Threat modeling has the same structural risk. A platform optimized to generate volume, without a mechanism for correlating findings against real threat intelligence or validating them against an actual attack attempt, produces a list that looks thorough and functions as noise.
For enterprise security teams at regulated organizations, this isn’t an abstract concern. A finding list that can’t be prioritized by credible business risk still has to be triaged by someone, and that triage work is exactly the bottleneck automation was supposed to remove.
What Risk-Based Architecture Analysis Actually Requires
Closing the gap between “theoretically possible” and “worth acting on” requires two things most generic automation doesn’t provide: a consistent tie between technical findings and business impact, and a way to correlate hypothesized attack paths against how adversaries actually behave rather than a static category list.
This is precisely the structure PASTA (Process for Attack Simulation and Threat Analysis) was designed around. Fork implements that methodology directly rather than layering automation on top of a generic framework. Business objectives and technical scope are established before component-level analysis begins, so every finding that follows can be evaluated against a business consequence that was already defined, not one added retroactively to justify a severity label.
How Fork Delivers Credible Attack Path Insight
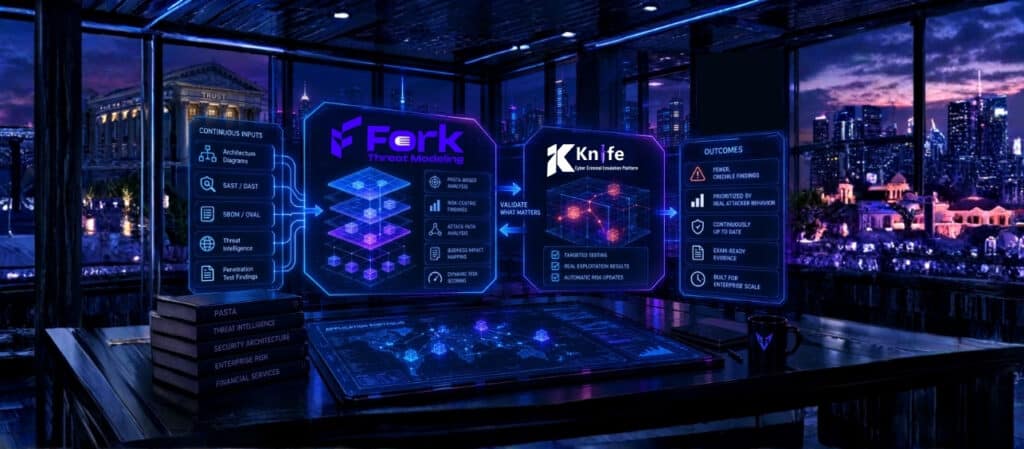
Fork’s architecture-level analysis draws on live threat intelligence and full-stack vulnerability data to correlate hypothesized attack paths against what’s actually being observed, rather than treating every theoretical path as equally worth flagging. Its dynamic residual risk scoring recalculates automatically as new findings, tests, and threat intelligence arrive, so a finding’s priority reflects current exposure instead of a static score assigned once and left stale.
The clearest expression of this credibility-first design is Fork’s integration with Knife, VerSprite’s AI-led, human-on-the-loop adversarial testing platform. From inside a Fork threat model, a security architect can request on-demand testing of a specific hypothesized weakness. Knife runs the assessment, and the result, confirmed exploitable or not, flows back into the model automatically, updating the application’s residual risk score. That loop is the difference between a platform that scores theoretical findings and one that can tell an architect which findings have actually been demonstrated to hold up.
Built for Security Architecture, Not Just Vulnerability Aggregation
A meaningful share of tools in this category operate primarily by ingesting scanner output and re-presenting it with a security label attached. Fork’s analysis starts a level higher, at the architecture itself: trust boundaries, data flows, and component decomposition, the same artifacts a manual PASTA-based review would examine, generated and kept current automatically. Vulnerability data from SAST, DAST, software composition analysis, SBOM and OVAL feeds, and manual penetration test findings feeds into that architectural model rather than substituting for it, which is what allows Fork to explain not just that a vulnerability exists, but how it connects to a broader attack path across the system’s actual design.
Built for Regulated Enterprise Environments
For security architects and CISOs operating under compliance obligations, the platform requirements extend beyond analysis quality. Fork Enterprise supports unlimited applications and teams, full integration support, SSO, granular access controls, and audit logging- the baseline a regulated organization needs to run threat modeling as a governed, portfolio-wide program rather than an ad hoc exercise applied inconsistently across systems. Because findings are continuously correlated rather than reconstructed at review time, the evidence trail those programs need for internal governance or external audit exists as a byproduct of ongoing use rather than a separate deliverable assembled under deadline pressure.
Getting Started
Fork is available as a free Community edition supporting a single application threat model with SBOM or OVAL-based vulnerability ingestion, a reasonable way to evaluate the platform’s analysis quality against one system before a broader rollout. Fork Enterprise unlocks the full platform across an application portfolio. Fork Enterprise PT adds on-demand adversarial testing through Knife and VerSprite’s BREAKERS offensive security team, for organizations that want validated risk, not just modeled risk. Organizations that want the same PASTA-based methodology delivered as expert-led engagement rather than a self-service platform can find that through VerSprite’s Threat Modeling as a Service offering instead.
Frequently Asked Questions
Share
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /