Penetration Testing Services
Manual, Risk-Based Penetration Testing for Networks, Applications, APIs, Mobile, and Cloud
Build a Tailored Penetration Testing Engagement- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
What Is Penetration Testing?
Penetration testing (pen testing) is an authorized, simulated attack against an organization’s systems, applications, and networks, performed by security professionals to find exploitable vulnerabilities, prove what an attacker could actually achieve with them, and guide remediation before real attackers find them.
A vulnerability scan lists potential weaknesses. A penetration test confirms which ones are exploitable, chains them together the way an attacker would, and shows the business impact — what data, systems, or transactions an attacker could reach.
VerSprite delivers manual, risk-based penetration testing led by experienced offensive security practitioners, with CREST-accredited web and mobile application security testing. Every engagement is scoped around your environment, your threat exposure, and the assets that matter most to your business.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
What Risk-Based Penetration Testing Means at VerSprite
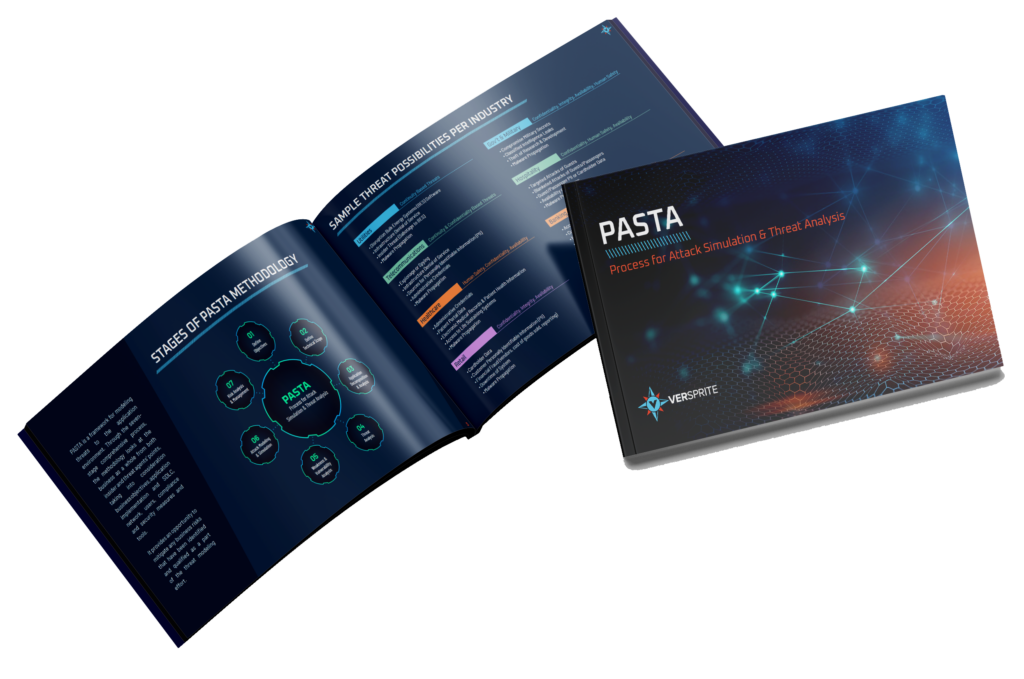
Most penetration tests rate findings by technical severity alone. VerSprite’s testing is informed by PASTA (Process for Attack Simulation and Threat Analysis), the risk-centric threat modeling methodology co-created by VerSprite CEO Tony UcedaVélez. In practice, that changes three things:
- What gets tested hardest. Testing effort concentrates on the attack paths most likely to be used against your organization and the assets whose compromise would hurt most.
- How findings are prioritized. Each finding is rated by technical severity (CVSS) and business impact, so a medium-severity flaw that exposes payment data outranks a high-severity issue on an isolated test server.
- What leadership receives. Reports explain risk in business terms, not just a list of CVEs.
Illustrative Example: How Business Impact Changes Priority
An example of risk-based prioritization in a typical API engagement.
A tester finds two issues in a customer-facing platform:
- An outdated library with a known high-severity CVE on an internal admin tool reachable only from a restricted network segment.
- A broken object-level authorization (BOLA) flaw in the customer API that lets one logged-in customer retrieve another customer’s account records by changing an ID.
A scanner-driven report lists the first as more severe. A risk-based test flags the second as the priority: it’s reachable by any customer, trivially exploitable at scale, and exposes regulated personal data. Both get fixed; the order is what changes.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Types of Penetration Testing We Perform
Network Penetration Testing (External and Internal)
External testing targets internet-facing systems — perimeter firewalls, VPNs, exposed services — as an outside attacker would. Internal testing starts inside the network to show how far an attacker with a foothold could move, escalate privileges, and reach critical systems.
Web Application Penetration Testing
Testing of websites, portals, and web platforms for vulnerabilities in code, configuration, and business logic, including injection, cross-site scripting, broken authentication and access control, and remote code execution. Aligned to the OWASP Web Security Testing Guide and ASVS. See Web Application Security Services.
API Penetration Testing
Assessment of REST and GraphQL APIs for authentication, authorization, input validation, and business logic flaws, including broken object-level authorization, excessive data exposure, and injection — mapped to the OWASP API Security Top 10.
Mobile Application Penetration Testing
Testing of iOS and Android apps for insecure data storage, weak transport security, flawed authentication, and vulnerabilities in the backend APIs they depend on, aligned to OWASP MASVS. See Mobile Security Testing.
Cloud Penetration Testing
Assessment of AWS, Azure, and Google Cloud environments for identity and access management weaknesses, misconfigured storage and networking, exposed services, and privilege escalation paths across hybrid and cloud-native infrastructure.
SAP Penetration Testing
Review of the SAP landscape — NetWeaver application servers, clients, and the layers between them — with recommendations on SAP Segregation of Duties to strengthen SAP profiles and avoid common security misconceptions.
Testing Approaches: Black Box, Gray Box, and White Box
- Black box: the tester starts with no internal knowledge, like an outside attacker. Most realistic, least thorough per hour.
- Gray box: the tester has partial knowledge, such as user credentials or architecture diagrams. The most common balance of realism and depth.
- White box: the tester has full access to architecture, configuration, and sometimes source code. Most thorough, best for finding deep logic and design flaws.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
CREST-Accredited Application Security Testing
VerSprite is CREST-accredited for web and mobile application security testing. CREST is an international accreditation body for the technical security industry; accreditation requires audited testing methodologies, data handling, and quality processes. For buyers, it is independent evidence that the testing team and process meet a recognized standard.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Industries We Serve
VerSprite delivers Penetration Testing across industries where security failures translate directly to financial loss, safety risk, or regulatory exposure.
Financial Services & FinTech
-
Identify exploitable vulnerabilities in online banking platforms, mobile apps, and payment systems
-
Test APIs, authentication mechanisms, and transaction workflows for security weaknesses
-
Assess cloud and hybrid infrastructure supporting financial services operations
-
Provide actionable remediation guidance aligned to regulatory and compliance expectations
Healthcare & Life Sciences
-
Identify vulnerabilities exposing ePHI, clinical systems, and research platforms
-
Test web applications, patient portals, and connected medical technologies
-
Assess internal and external network security controls protecting healthcare environments
-
Deliver remediation guidance aligned to HIPAA and healthcare security frameworks
SaaS & Technology Providers
-
Test cloud-native applications, APIs, and microservices for exploitable weaknesses
-
Assess authentication flows, role-based access controls, and tenant isolation
-
Identify vulnerabilities in CI/CD pipelines and supporting infrastructure
-
Provide remediation insights to strengthen customer trust and enterprise security posture
Retail & E-Commerce
-
Identify vulnerabilities in e-commerce platforms, payment processing systems, and mobile apps
-
Test checkout flows, customer account security, and third-party integrations
-
Assess infrastructure resilience during high-traffic and peak transaction periods
-
Deliver prioritized remediation guidance to protect customer data and brand reputation
Manufacturing & Critical Infrastructure
-
Identify vulnerabilities across IT networks and connected operational environments
-
Test segmentation controls between enterprise systems and OT infrastructure
-
Assess external exposure of production systems and remote access pathways
-
Provide actionable remediation steps to reduce operational disruption risk
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Standards and Frameworks We Follow
- Penetration Testing Execution Standard (PTES) — engagement structure from pre-engagement through reporting
- NIST SP 800-115 — technical guide to information security testing and assessment
- OWASP Web Security Testing Guide (WSTG) and Application Security Verification Standard (ASVS) — web application testing coverage and verification requirements
- OWASP API Security Top 10 and OWASP MASVS — API and mobile application testing
- MITRE ATT&CK — mapping of post-exploitation techniques for detection teams
- CVSS — standardized technical severity scoring, paired with VerSprite’s business-impact rating
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Penetration Testing for Compliance
Penetration testing is required or expected by most major security frameworks. VerSprite testing produces evidence for:
- PCI DSS — Requirement 11.4 calls for internal and external penetration testing at least annually and after significant changes, plus segmentation testing.
- SOC 2 — auditors commonly expect annual penetration testing as evidence for security criteria.
- HIPAA — testing supports the technical evaluation and risk analysis expected for systems handling ePHI.
- ISO/IEC 27001 — testing supports technical vulnerability management and security testing controls.
- DORA and other financial regulations — testing supports digital operational resilience requirements. For threat-led testing, see Red Teaming.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Pentesting FAQ: Our Penetration Tester Answers the Internet’s Most Asked Questions
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Stages of a VerSprite Penetration Test
- Pre-engagement and scoping. Define scope, objectives, testing approach, rules of engagement, and authorizations so testing is safe and legal.
- Reconnaissance. Map the attack surface, entry points, infrastructure, and digital footprint.
- Threat modeling and vulnerability analysis. Use what was learned to identify and prioritize the attack paths most relevant to your environment.
- Exploitation. Attempt to exploit weaknesses in a controlled, monitored way, chaining issues to show what an attacker could actually achieve.
- Post-exploitation. Assess real-world impact: reachable data and systems, privilege escalation, and lateral movement toward critical assets.
- Reporting. Document each finding with evidence, CVSS and business-impact ratings, and prioritized remediation guidance for technical teams and leadership.
- Remediation support and retesting. Retest after fixes to confirm vulnerabilities are resolved and no new issues were introduced.
What You Get
- An executive summary that explains risk in business terms
- Detailed findings with reproduction steps and evidence
- Severity ratings combining CVSS and business impact
- Prioritized, actionable remediation guidance
- Retesting to validate fixes
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Point-in-Time Testing or Continuous PTaaS?
This page covers scoped, point-in-time penetration testing engagements — the right choice for annual compliance testing, pre-launch assessments, and major changes. If your environment changes frequently, Penetration Testing as a Service (PTaaS) provides recurring, prioritized testing across applications, networks, APIs, cloud, and internal systems.
Frequently Asked Questions
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Related Services and Resources
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Find the Vulnerabilities That Actually Matter
VerSprite penetration testing shows you which weaknesses an attacker could exploit, what they could reach, and what to fix first.
