Threat Modeling as a Service (TMaaS)
On-Demand PASTA Threat Models, Delivered by the Team That Created the Methodology
Scope a TMaaS Engagement- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
What Is Threat Modeling as a Service?
Threat Modeling as a Service (TMaaS) is a managed service in which an external team of threat modeling specialists builds and maintains threat models for an organization’s applications and systems — identifying how each could be attacked, which threats matter most to the business, and which countermeasures to prioritize — without the organization having to staff and train that capability in-house.
VerSprite delivers TMaaS using PASTA (Process for Attack Simulation and Threat Analysis), the risk-centric threat modeling methodology co-created by VerSprite CEO Tony UcedaVélez. Your teams get finished, risk-ranked threat models for new and existing applications, delivered on demand or on a continuous cycle that keeps pace with development.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
What Is Threat Modeling?
Threat modeling is the practice of analyzing a system’s design from an attacker’s perspective to identify threats, weaknesses, and attack paths before they reach production. A widely used way to frame it is Adam Shostack’s Four Question Framework, also reflected in the Threat Modeling Manifesto:
- What are we working on?
- What can go wrong?
- What are we going to do about it?
- Did we do a good job?
PASTA answers those questions with a business-risk lens: it starts from business objectives, uses threat intelligence to decide which threats are realistic, and ranks countermeasures by business impact rather than by threat category alone.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
What You Get: A PASTA Threat Model, Stage by Stage
Every VerSprite TMaaS threat model produces concrete outputs at each of PASTA’s seven stages:
| Service | Best for |
|---|---|
| Threat Modeling as a Service (TMaaS) | Ongoing or on-demand threat models delivered by VerSprite as a managed service |
| Application Threat Modeling | An in-depth threat model of a single application or system |
| Enterprise Threat Modeling | Building a threat modeling program across a large application portfolio |
| Continuous Threat Modeling with Fork | Keeping threat models current in a platform as systems change |
| Organizational Threat Modeling | Threat-led attack simulation against the organization as a whole |
| PASTA Threat Modeling | Understanding and adopting the PASTA methodology itself |
For the full methodology, see PASTA Threat Modeling.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Delivery Models
- Point-in-time threat models for a specific application, release, or architecture change.
- Continuous TMaaS with threat models built for new projects and updated as designs change, on an agreed cadence.
- Hybrid in which VerSprite builds models alongside your security team and reviews models they create.
- Capability building in which VerSprite delivers models while training your team in PASTA, so threat modeling becomes self-sustaining over time.
Engagements cover web applications, mobile applications, APIs, cloud architectures, and complex enterprise systems, and can start at any point from early design through to systems already in production.
Built on Fork, VerSprite’s Threat Modeling Platform
Threat models are living documents, and keeping them current is where most programs fail. VerSprite TMaaS can be delivered in Fork, VerSprite’s PASTA threat modeling platform, so models stay maintained, searchable, and consistent across your portfolio instead of living in slide decks and spreadsheets. See Continuous Threat Modeling with Fork.
When TMaaS Makes Sense
- Development velocity outpaces your security team’s ability to review designs.
- You need threat models for compliance or customer assurance, but don’t have trained threat modelers.
- You’re launching a new product, re-architecting for cloud, or integrating new third-party services.
- Your existing threat models are inconsistent across teams or out of date.
- You want to build an internal threat modeling program and need experienced practitioners to start it.
Threat Modeling and Compliance
Threat modeling is required or expected by a growing set of security frameworks and regulations:
- NIST Secure Software Development Framework (SSDF, SP 800-218) — calls for risk modeling such as threat modeling during software design.
- FDA premarket cybersecurity guidance — expects threat modeling as part of the security risk management documentation for medical devices.
- OWASP SAMM — includes threat assessment and threat modeling as a core practice for measuring software security maturity.
- EU Cyber Resilience Act — requires manufacturers of products with digital elements to perform cybersecurity risk assessments.
- PCI DSS, HIPAA, and SOC 2 — threat models provide documented evidence of design-level risk analysis for systems handling regulated data.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
PASTA vs. STRIDE: Why VerSprite Uses PASTA
STRIDE, developed at Microsoft, is a threat categorization model: it classifies threats as Spoofing, Tampering, Repudiation, Information disclosure, Denial of service, or Elevation of privilege. It’s useful for brainstorming threats against individual components. PASTA is a full risk-centric process: it starts from business objectives, uses threat intelligence to focus on realistic threats, validates them through attack modeling, and ranks results by business impact. STRIDE categories can be used inside PASTA’s threat analysis stage; PASTA adds the business context that tells you which threats to fix first. For tool comparisons, see Threat Modeling Tools Compared.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Which VerSprite Threat Modeling Service Fits?
| Service | Best for |
|---|---|
| Threat Modeling as a Service (TMaaS) | Ongoing or on-demand threat models delivered by VerSprite as a managed service |
| Application Threat Modeling | An in-depth threat model of a single application or system |
| Enterprise Threat Modeling | Building a threat modeling program across a large application portfolio |
| Continuous Threat Modeling with Fork | Keeping threat models current in a platform as systems change |
| Organizational Threat Modeling | Threat-led attack simulation against the organization as a whole |
| PASTA Threat Modeling | Understanding and adopting the PASTA methodology itself |
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Industries We Serve
VerSprite delivers TMaaS across industries where security failures translate directly to financial loss, safety risk, or regulatory exposure: financial services and FinTech, healthcare and life sciences, SaaS and technology providers, retail and e-commerce, and manufacturing and critical infrastructure.
Free eBook
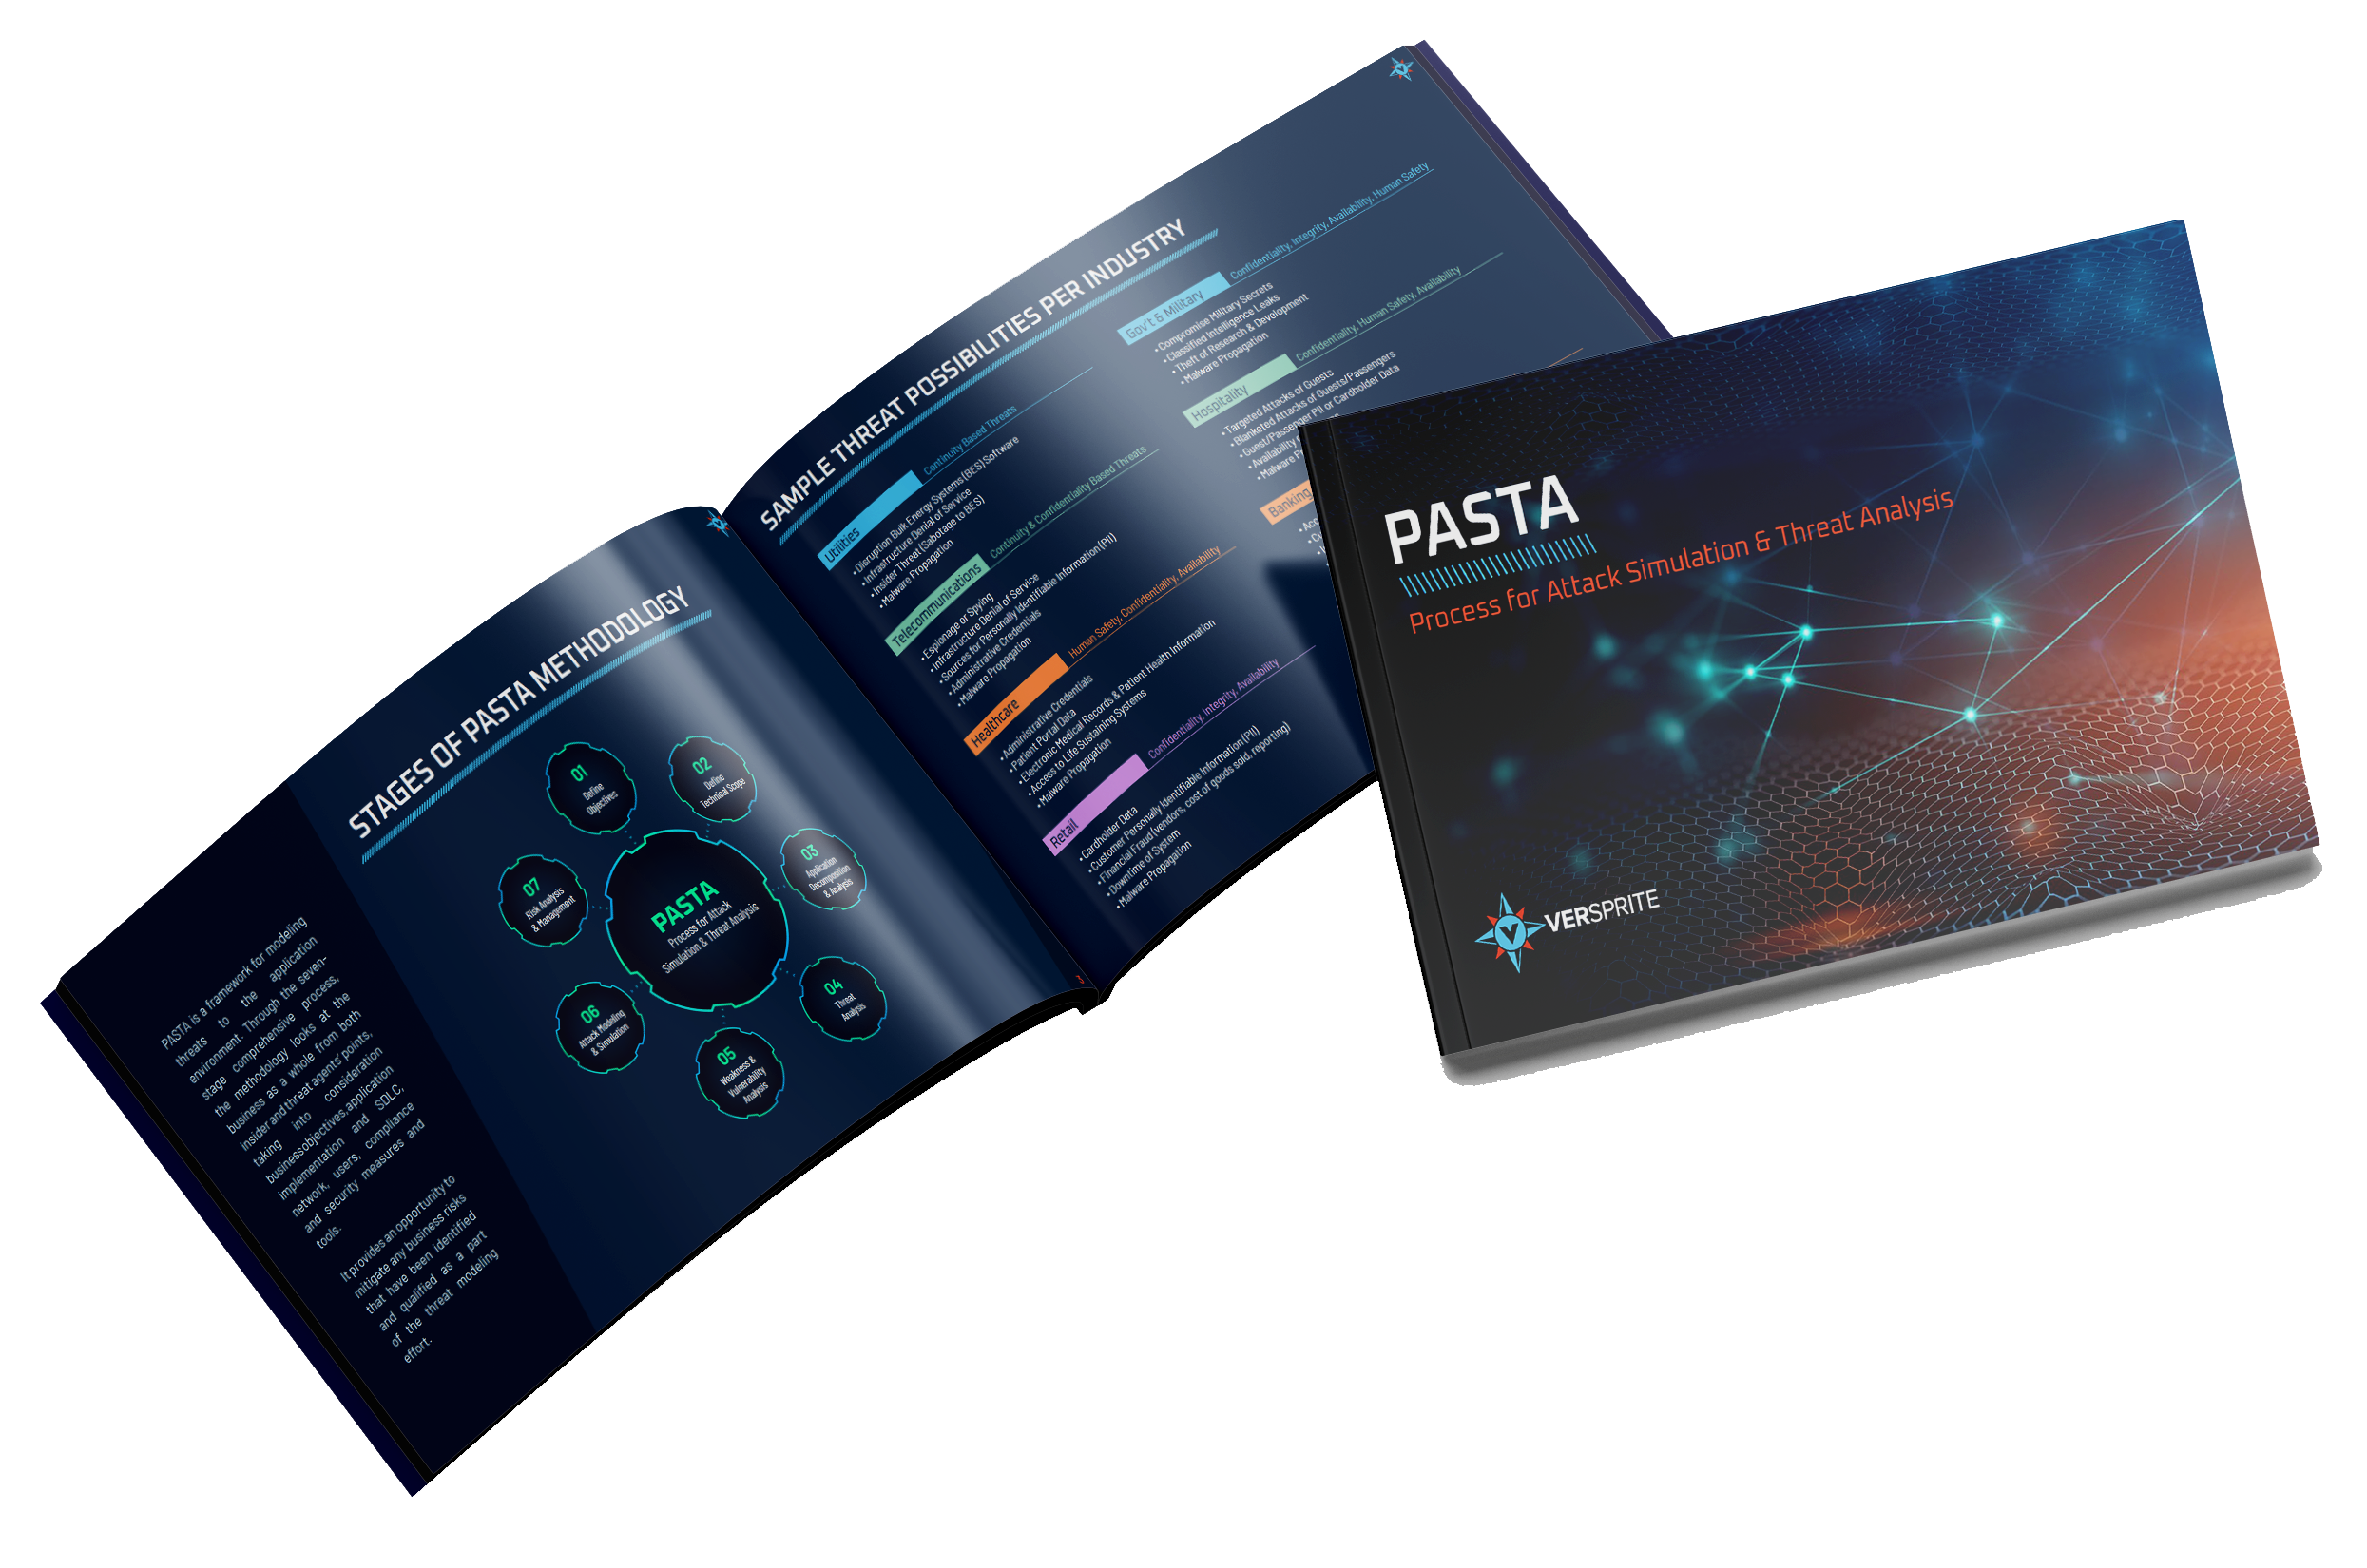
Free eBook: PASTA Risk-Based Threat Modeling
PASTA treats cyber threat mitigation as a business problem first. The eBook walks through the process for analyzing the attacks that could exploit your vulnerabilities and mapping them to threat scenarios focused on the application as a business asset.
Frequently Asked Questions
Cyber Threat Modeling as a Service (TMaaS) is a scalable, on-demand approach to identifying, analyzing, and mitigating security threats. VerSprite delivers TMaaS so organizations can leverage external experts, PASTA-based methodology, and purpose-built tooling instead of building internal threat modeling capabilities from scratch.
Traditional threat modeling is often performed internally as a one-time or periodic activity, while TMaaS delivers continuous or on-demand threat modeling through specialized providers. This lets organizations scale security efforts without maintaining dedicated in-house expertise.
Key benefits include scalability without increasing internal headcount, faster time-to-delivery and reduced operational overhead, access to specialized expertise and methodologies, improved consistency across projects, and cost-effectiveness compared to building internal teams.
A TMaaS engagement typically includes application and system architecture analysis, threat identification and attack surface evaluation, risk prioritization based on business impact, mitigation strategies and validation, and documentation for compliance and reporting.
Organizations should consider TMaaS when security expertise is limited or overstretched, development speed exceeds internal security capabilities, regulatory requirements demand formal threat modeling, or projects require specialized or evolving threat analysis.
TMaaS helps identify vulnerabilities early in the SDLC, uncover design flaws, and evaluate emerging attack techniques. This proactive approach reduces risk and prevents costly remediation later in development.
Yes. TMaaS can integrate into DevSecOps workflows by providing ongoing threat analysis, supporting CI/CD pipelines, and enabling continuous security validation throughout development.
VerSprite runs TMaaS on Fork, its PASTA-based platform, to bring threat modeling automation to every engagement. Fork builds a risk-centric threat model in under two hours and keeps it current from Sprint 1 by ingesting SAST, DAST, SCA, penetration testing, and threat intelligence data. It maps findings to industry taxonomies and flags residual risk changes against quality gates. VerSprite’s analysts then focus on attack simulation, validation, and remediation guidance. Learn more at forktm.com.
VerSprite’s TMaaS uses PASTA (Process for Attack Simulation and Threat Analysis) — the risk-based methodology VerSprite CEO Tony UcedaVélez co-created — which focuses on real-world attack simulation and risk-based prioritization aligned to business impact.
TMaaS can identify application and infrastructure vulnerabilities, business logic flaws, API and integration risks, advanced attack paths and threat scenarios, and emerging threats based on real-world intelligence.
VerSprite delivers a risk-based, attacker-centric approach using the PASTA methodology, combining threat intelligence, attack simulation, and business context to prioritize the most critical risks and provide actionable remediation guidance.
TMaaS provides external expertise, scalability, and advanced tools without the need to hire and maintain internal teams. In-house threat modeling requires dedicated resources, training, and ongoing investment, which can be costly and difficult to scale.
Organizations should use TMaaS when launching new applications, undergoing digital transformation, scaling development teams, or needing continuous security insights without expanding internal security operations.
Yes. TMaaS is typically more cost-effective than building and maintaining an in-house threat modeling team, as it reduces staffing costs, tooling investments, and operational overhead while delivering expert-driven results.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Related Services and Resources
Continuous Threat Modeling with Fork — Keep threat models current as systems change.
Application Threat Modeling — In-depth threat models for individual applications.
PASTA Threat Modeling Tools — How threat modeling platforms support the PASTA methodology.
Threat Modeling Tools Compared — A side-by-side comparison of leading threat modeling platforms.
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
- /
Resources
Get Threat Models
Your Teams Will Actually Use
VerSprite TMaaS gives your teams finished, risk-ranked threat models from the people who wrote the methodology — so security decisions get made at design time, not after an incident.
